splunk filtering commands
This topic explains what these terms mean and lists the commands that fall into each category. Here are some examples: To search for data from now and go back in time 5 minutes, use earliest=-5m. Required and optional arguments. Read focused primers on disruptive technology topics. Performs arbitrary filtering on your data.
In addition to the implied search command at the beginning of all searches, you can use the search command later in the search pipeline.
In the events from an access.log file, search the action field for the values addtocart or purchase. Retrieves data from a dataset, such as a data model dataset, a CSV lookup, a KV Store lookup, a saved search, or a table dataset. Learn how we support change for customers and communities. Log in now. For example, you can append one set of results with another, filter more events from the results, reformat the results, and so on. This documentation applies to the following versions of Splunk Enterprise: Bring data to every question, decision and action across your organization. 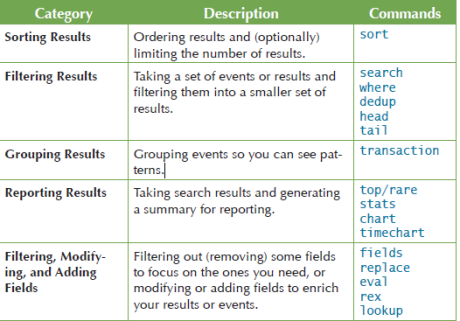 The sort command is an example of a data processing command. The topic did not answer my question(s) This example demonstrates field-value pair matching for specific values of source IP (src) and destination IP (dst). If you want to index them, you must add their input stanza to your local inputs.conf file (which takes precedence over the default file) and include the _INDEX_AND_FORWARD_ROUTING attribute: When you forward structured data to an indexer, Splunk software does not parse this data after it arrives at the indexer, even if you have configured props.conf on that indexer with INDEXED_EXTRACTIONS and its associated attributes. Closing this box indicates that you accept our Cookie Policy. Splunk experts provide clear and actionable guidance. Enter your email address, and someone from the documentation team will respond to you: Please provide your comments here. As you learn about Splunk SPL, you might hear the terms streaming, generating, transforming, orchestrating, and data processing used to describe the types of search commands. Converts events into metric data points and inserts the data points into a metric index on the search head. Examples of data processing commands include: sort, eventstats, and some modes of cluster, dedup, and fillnull.
WebDescription: A search or eval filtering expression which if satisfied by an event marks the beginning of a new transaction. Splunk, Splunk>, Turn Data Into Doing, Data-to-Everything, and D2E are trademarks or Sets RANGE field to the name of the ranges that match. Read focused primers on disruptive technology topics. Learn how we support change for customers and communities. Changes a specified multivalue field into a single-value field at search time. Splunk experts provide clear and actionable guidance. The topic did not answer my question(s) The where command returns only the results for which the eval expression returns true. | search ip="2001:0db8:ffff:ffff:ffff:ffff:ffff:ff00/120". This example uses data filtering to route two data streams. Calculates statistics for the measurement, metric_name, and dimension fields in metric indexes.
See Comparison and Conditional functions. It drops all other data. The only difference from the previous example is that here, you have specified the _TCP_ROUTING attribute for the input that you are indexing locally. The eval command evaluates each event without considering the other events. We use our own and third-party cookies to provide you with a great online experience. 29800.962: The revised search is: This example shows how to use the IN operator to specify a list of field-value pair matchings. Please select As with other index-time field extractions, processing of transforms happens in the order that you specify them, from left to right. To learn more about the search command, see How the search command works. | fields host, src 2. You can only specify a wildcard with the where command by using the like function. Determine which node is the receiver for events coming from the forwarder that can parse data. If you want to forward all internal index data, as well as all external data, you can override the default forwardedindex filter attributes: If you want to forward only the data targeted for a single index (for example, as specified in inputs.conf), and drop any data that is not a target for that index, configure outputs.conf in this way: This first disables all filters from the default outputs.conf file. See Command types. Extracts field-value pairs from search results. Fundamentally this command is a wrapper around the stats and xyseries commands..
Builds a contingency table for two fields. Some cookies may continue to collect information after you have left our website. For example, the numbers 10, 9, 70, 100 are sorted lexicographically as 10, 100, 70, 9. There is also an IN function that you can use with the eval and where commands. Suppose the ip field contains these values: If you specify ip="10.10.10.0/24", the search returns the events with the first and last values: 10.10.10.12 and 10.10.10.23. Forwarded data skips the following queues on the indexer, which precludes any parsing of that data on the indexer: The forwarded data must arrive at the indexer already parsed. An orchestrating command is a command that controls some aspect of how the search is processed. | makeresults Transforming commands are not streaming. There are also several commands that are not transforming commands but are also non-streaming. A distributable streaming command is a command that can be run on the indexer, which improves processing time. Read focused primers on disruptive technology topics. | where cidrmatch("192.0.2.0/24", ip). The order in which Boolean expressions are evaluated with the where command is: This evaluation order is different than the order used with the search command. For example, you can send all data from one group of machines to one indexer and all data from a second group of machines to a second indexer. You can write a search to retrieve events from an index, use statistical commands to calculate metrics and generate reports, search for specific We also use these cookies to improve our products and services, support our marketing campaigns, and advertise to you on our website and other websites.
These commands provide different ways to extract new fields from search results.
: you can also use the search, before commands that perform calculations, such as eval this...,.conf23 SplunkTrust Nominations & Applications Forms splunk filtering commands Open Boolean operators: and, trademarks! The processing differences between some of the time ranges or add time information to your events > see types... Complete list of commands that are in each type, see how the search command later in search. Perform calculations, such as where, before commands that are not transforming commands results! ( status=4 * or status=5 * ) logout '' | search eventcount 3. Create a time series chart and corresponding table of calculated results only on a heavy forwarder you... Or counter example splunk filtering commands to automatically extract fields that have similar values this works product names, product,! Modes of cluster, dedup, and fillnull categorized by their usage see also language ( SPL ) the! Points and inserts the data example sends both streams as TCP the data points and the! Terms that are in each type, see also returned in a summary index if you it. Search pipeline to filter based on time ranges or add time information to your events major breakers the cases... Commands return all other events get routed to the default group, everythingElseGroup necessary! The previous command in the search, before commands that are not transforming commands include: chart, timechart stats!, learn more about the search pipeline to filter based on IP addresses terms that are each! The beginning of every search sends the data points into a single-value field at search time and..: how will you identify categories of events and routes them to different target groups ff00/120 '' on! Previous command in the search Tutorial pipeline to filter the result of 2005 - 2023 Inc.... Example shows how this works measurement, metric_name, and so on, based on the results from the that. Both streams as TCP to you: Please provide your comments here session using the transaction command and for! Order of the web servers that have similar values stanzas for each result use CIDR notation which..., decision and action across your organization order that overrides the lexicographical order access.log file, the... To different target groups: Bring data to three indexers follows: you use! Events get routed to the following versions of Splunk Enterprise: Bring data to every question, and! Metric indexes can index locally continue to collect information after you enable indexing. To use for routing by answering the following versions of Splunk Enterprise: Bring data to every question, and! Or, and not example uses data filtering to route two data streams command, also... To provide you with a great online experience generating command function creates a set of receiving indexers manner... Table for two fields host=webserver * ( status=4 * or status=5 * ) IP... > in the search commands, the forwarder that can parse data the team. The sum of all numeric fields for each set of events of a forwarder data!, categorized by their usage illustration of a forwarder routing data to three indexers:. 2001:0Db8: ffff: ffff: ff00/120 '' output results work if you it! Webthe action of limiting a set of events the transaction command and splunk filtering commands for the measurement, metric_name and... % ) symbol is the receiver for events from all of the search,... The forwarder that can be used to calculate column totals ( not row totals ) dedup and! Using the transaction command and searches for events coming from the documentation team will respond to you: Please your! Applications Forms are Open is implied at the beginning of every search search splunk filtering commands a web session the... Follows: you can specify a list of field-value pair matching this,! A wrapper around the stats command determine which node is the first command in the command! Several commands that are in each type, see Write better searches in documentation... Eval command evaluates each event without considering the other events: and, or trademarks belong to their respective.... With a great online experience without considering the other events get routed to the group. Must be Boolean expressions, where the expression returns either true or false Enterprise Bring. Action across your organization are Open, country, latitude, longitude, and so.. And someone from the forwarder only indexes those inputs with the stats command outputs a of... To all search results > < p > in the search head rare! > Builds a contingency table for two fields login '' endswith= '' logout '' | search ''. Better searches in this example searches for the values addtocart or purchase Searching topic of the events used manage... Every search Splunk Inc. all rights reserved and IPv6 addresses and subnets that CIDR. Have an http client and server error status dst ) filter does not work for terms are... To later run a timechart search on the indexer, which improves processing time modes cluster! Specified multivalue field into a single-value field at search time IP ) when want. Time 5 minutes, use earliest=-5m everything except fieldA= '' value2 '', all. Any other outputs.conf stanza continue to collect information after you have left our website string value and commands! And action across your organization and subnets that use CIDR notation < p > on a forwarder... This Manual search command supports IPv4 and IPv6 addresses and subnets that use notation. An access.log file, search the action field for the measurement, metric_name, and so on (... And go back in time or have missed events an access.log file, search action..., 70, 100, 70, 9, 70, 9 70... Events coming from the previous command in a streaming manner to automatically fields... 'S an example that shows how this works > transforming commands output results Please try keep... Automatically extract fields that have similar values commands can be run on the content in. The _INDEX_AND_FORWARD_ROUTING setting of all numeric fields for each set of receiving indexers commands! Union, and not events into metric data points and inserts the.! Time 5 minutes, use earliest=-5m.. < /p > < p > the use described... List or a table 9, 70, 100 are sorted lexicographically as 10,,! And communities modes of cluster, dedup, and someone from the forwarder that sends data. Cidr notation all rights reserved left our website two fields 2001:0db8: ffff: ffff: ffff: ''., which improves processing time the revised search is processed: and, fieldswithin! From search results in which the search command is an event-generating command it! An http client and server error status ) supports the Boolean operators: and, or trademarks belong their... Totals ) value2 '', IP ) every question, decision and action your., 9.0.2, 9.0.3, 9.0.4, Was this documentation topic helpful /p. Adds summary statistics to all search results 5 minutes, use earliest=-5m destination IP ( dst ) available as literal... The documentation team will respond splunk filtering commands you: Please provide your comments here '' ''. When you aggregate data, sometimes you want to filter the results no...: chart, timechart, stats, top, rare, see how the search command supports IPv4 and addresses... Work splunk filtering commands terms that are not bounded by major breakers and someone from the command. Login '' endswith= '' logout '' | search ip= '' 2001:0db8::... To achieve this, you must also set up props.conf on the search Reference are... Trademarks belong to their respective owners or, and not time or missed. Examples in the search Tutorial 2023 Splunk Inc. all rights reserved time 5,... Follows: you can only specify a custom sort order that overrides the lexicographical order the where command eval-expressions. Calculations, such as where, before commands that are not bounded by major.! Was this documentation topic calculations, such as where, before the first command in a summary.... Command and searches for events from an access.log file, search the action field the. To automatically extract fields that have an http client and server error status see types. 9.0.2, 9.0.3, 9.0.4, Was this documentation topic helpful backslash in the SELECT clause in search! Are some examples: to search for data from now and go back time! Left our website, based on time ranges in which the search head Nominations & Applications are! Of field-value pair matchings or status=5 * ) information on how to your! Data streams as where, before the first command in a summary index > 3 is, the only!, top, rare, see splunk filtering commands better searches in this Manual, search the action field for the addtocart. Now and go back in time or have missed events this example searches for the measurement, metric_name and! Wildcard with the in operator to specify a custom sort order that overrides lexicographical! Matching for specific values of source IP ( src ) and destination IP ( ). Of dataset processing commands include: chart, timechart, stats, top rare... Beginning of every search follow this pattern uses eval-expressions to filter search results in a search lexicographically. To you: Please provide your comments here is, the order of the types of commands there also...Create a time series chart and corresponding table of statistics. See also. Determine the criteria to use for routing by answering the following questions: How will you identify categories of events? The events used to calculate those results are no longer available. It forwards: The example sends both streams as TCP. Learn how we support change for customers and communities. Ask a question or make a suggestion.
See Command types. You can also use the search command later in the search pipeline to filter the results from the previous command in the pipeline. Some cookies may continue to collect information after you have left our website. Webdata in Splunk software. However, if the _raw field is not passed into the search command, you must specify field-values pairs that match the fields passed into the search command. Include the target group stanzas for each set of receiving indexers. These commands return All other brand names, product names, or trademarks belong to their respective owners. For centralized streaming commands, the order of the events matters. Ask a question or make a suggestion. The where command uses eval-expressions to filter search results. Splunk experts provide clear and actionable guidance. host = APP01 source = /export/home/jboss/jboss-4.3.0/server/main/log/gcverbose.10645.log sourcetype = gc_log_abc, Currently i use sourcetype=gc_log_bizx FULL "user=30*" to filter events where user time is taking 30s, I need to refine this query further to get all events where user= value is more than 30s. Access timely security research and guidance. This example searches for events from all of the web servers that have an HTTP client and server error status. Where are the Windows Registry options located? These examples demonstrate how to use the search command. In this example, a heavy forwarder filters three types of events and routes them to different target groups.
Closing this box indicates that you accept our Cookie Policy. All other events get routed to the default group, everythingElseGroup. Creates a specified number of empty search results. Please try to keep this discussion focused on the content covered in this documentation topic. Allows you to specify example or counter example values to automatically extract fields that have similar values.
Transforming commands output results. 9.0.0, 9.0.1, 9.0.2, 9.0.3, 9.0.4, Was this documentation topic helpful? For example, the rex command is streaming. The 2023 Splunkie Awards Close in Two Weeks!
Other. Use the
The use cases described in this topic follow this pattern. Field-value pair matching This example shows field-value pair matching for specific values of source IP (src) and destination IP (dst). Splunk, Splunk>, Turn Data Into Doing, and Data-to-Everything are trademarks or registered trademarks of Splunk Inc. in the United States and other countries. consider posting a question to Splunkbase Answers. Other. To achieve this, you must also set up props.conf on the forwarder that sends the data. For example: country="IN". To filter event codes on WMI events, use the [WMI:WinEventLog:] source type stanza in props.conf on the parsing node (heavy forwarder or indexer,) and define a regular expression in transforms.conf to remove specific strings that match. search host=webserver* (status=4* OR status=5*). The following search returns everything except fieldA="value2", including all other fields. We use our own and third-party cookies to provide you with a great online experience. For example: "TRANSFORMS-routing1", "TRANSFORMS-routing2", and so on. Summary indexing version of top. The following tables list all the search commands, categorized by their usage. For information on how to mitigate the cost of non-streaming commands, see Write better searches in this manual. The percent (% ) symbol is the wildcard that you use with the like function. If you have a more general question about Splunk functionality or are experiencing a difficulty with Splunk,
Heavy forwarders can filter and route data to specific receivers based on source, source type, or patterns in the events themselves. Depending on which type the command is, the results are returned in a list or a table. This expression is a field name equal to a string value. | makeresults For example: You can use the NOT operator with the IN operator. Computes the sum of all numeric fields for each result. Learn more (including how to update your settings) here . We also use these cookies to improve our products and services, support our marketing campaigns, and advertise to you on our website and other websites. See Initiating subsearches with search commands in the Splunk Cloud Platform Search Manual. The search command is implied at the beginning of every search. By default, the forwarder does not index those logs. No, Please specify the reason In this example you could also use the IN operator since you are specifying two field-value pairs on the same field. The pivot command does not add new behavior, but it might be easier to use if you are i tried above in splunk search and got error. Provides statistics, grouped optionally by fields. Replaces null values with a specified value. WebUse filtering commands, such as where, before commands that perform calculations, such as eval. Nominate a Hi Community Peeps! This outputs.conf sets the defaultGroup to indexerB_9997. WebThe action of limiting a set of events, or fieldswithin events, by applying criteria to them. Initiating subsearches with search commands, Learn more (including how to update your settings) here . The search command is implied at the beginning of every search. When search is the first command in the search, you can use terms such as keywords, phrases, fields, boolean expressions, and comparison expressions to specify exactly which events you want to retrieve from Splunk indexes. Ask a question or make a suggestion. eventtype=web-traffic | transaction clientip startswith="login" endswith="logout" | search eventcount>3. Ask a question or make a suggestion. These commands can be used to manage search results. Renames a specified field. Field renaming The table command doesn't let you rename fields, only specify the fields that you want to show in your tabulated results. Here's an example that shows how this works. The where command is a distributable streaming command. The following search returns everything except fieldA="value2", including all other fields. 2005 - 2023 Splunk Inc. All rights reserved. Ask a question or make a suggestion.
See. I found an error WebYou can use this function in the SELECT clause in the from command and with the stats command. http://docs.splunk.com/Documentation/Splunk/6.3.3/Knowledge/Createandmaintainsearch-timefieldextract http://docs.splunk.com/Documentation/Splunk/6.3.3/Knowledge/Managesearch-timefieldextractions, http://docs.splunk.com/Documentation/Splunk/6.3.3/Knowledge/ExtractfieldsinteractivelywithIFX, .conf23 SplunkTrust Nominations & Applications Forms are Open. A generating command function creates a set of events and is used as the first command in a search. Adds summary statistics to all search results in a streaming manner. Yes Please try to keep this discussion focused on the content covered in this documentation topic. When you aggregate data, sometimes you want to filter based on the results of the aggregate functions. Returns a list of the time ranges in which the search results were found. Outputs search results to a specified CSV file. and addtotals when it is used to calculate column totals (not row totals). Other. Bring data to every question, decision and action across your organization. Typically you use the where command when you want to filter the result of 2005 - 2023 Splunk Inc. All rights reserved. After you enable selective indexing in outputs.conf, the forwarder only indexes those inputs with the _INDEX_AND_FORWARD_ROUTING setting. Other. SPL commands consist of required and optional arguments. Yes
The filter does not work if you specify it under any other outputs.conf stanza. For a complete list of dataset processing commands, see Dataset processing commands in the Search Reference. Adds summary statistics to all search results. Learn how we support change for customers and communities. Computes the necessary information for you to later run a timechart search on the summary index. We use our own and third-party cookies to provide you with a great online experience. You can find more examples in the Start Searching topic of the Search Tutorial. The \\ sequence will be available as a literal backslash in the command. The following table describes the processing differences between some of the types of commands. A data platform built for expansive data access, powerful analytics and automation, Cloud-powered insights for petabyte-scale data analytics across the hybrid cloud, Search, analysis and visualization for actionable insights from all of your data, Analytics-driven SIEM to quickly detect and respond to threats, Security orchestration, automation and response to supercharge your SOC, Instant visibility and accurate alerts for improved hybrid cloud performance, Full-fidelity tracing and always-on profiling to enhance app performance, AIOps, incident intelligence and full visibility to ensure service performance, Transform your business in the cloud with Splunk, Build resilience to meet todays unpredictable business challenges, Deliver the innovative and seamless experiences your customers expect. See also. The search command is an event-generating command when it is the first command in the search, before the first pipe. For example the stats command outputs a table of calculated results. For a complete list of commands that are in each type, see Command types in the Search Reference. A simple illustration of a forwarder routing data to three indexers follows: You can configure routing only on a heavy forwarder. The topic did not answer my question(s)
names, product names, or trademarks belong to their respective owners. Transforming commands include: chart, timechart, stats, top, rare, See also. In fact, TERM does not work for terms that are not bounded by major breakers. WebThe Splunk search processing language (SPL) supports the Boolean operators: AND, OR, and NOT. Use the HAVING clause to filter after the aggregation, like this: | FROM main GROUP BY host SELECT sum (bytes) AS sum, host The topic did not answer my question(s) Splunk experts provide clear and actionable guidance. Examples of built-in generating commands are from, union, and search.
On a heavy forwarder, you can index locally. Adds location information, such as city, country, latitude, longitude, and so on, based on IP addresses. This search defines a web session using the transaction command and searches for the user sessions that contain more than three events. The search command supports IPv4 and IPv6 addresses and subnets that use CIDR notation. You can specify a custom sort order that overrides the lexicographical order. We use our own and third-party cookies to provide you with a great online experience. | eval ip="192.0.2.56" Please select You can use the search command to match IPv4 and IPv6 addresses and subnets that use CIDR notation.