sentinelone api documentation
This activity is most likely related to the deployment of a Python server or an application that needs to communicate over a network. SentinelOne API token limitations The API token is only available to view during token creation. Log in to the Perch app. These legitimate DLLs are used by the information stealer to collect data on the compromised hosts. Event category. Detects suspicious scheduled task creation, either executed by a non-system user or a user who is not administrator (the user ID is not S-1-5-18 or S-1-5-18-*). Powershell's uploadXXX functions are a category of methods which can be used to exfiltrate data through native means on a Windows host. Please find bellow a limited list of field types that are available with SentinelOne default EDR logs: And depending on the context of the log, additional content could be available, such as: For advanced log collection, we suggest you to use SentinelOne Deep Visibility kafka option, as described offered by the SentinelOne DeepVisibility integration. ", "{\"accountId\": \"551799238352448315\", \"activityType\": 4008, \"agentId\": \"997510333395640565\", \"agentUpdatedVersion\": null, \"applications\": null, \"comments\": null, \"createdAt\": \"2022-04-05T09:10:15.125572Z\", \"data\": {\"accountName\": \"corp\", \"computerName\": \"CL001234\", \"escapedMaliciousProcessArguments\": null, \"fileContentHash\": \"08731ccac0d404da077e7029062f73ca3d8faf61\", \"fileDisplayName\": \"Run SwitchThemeColor.ps1.lnk\", \"filePath\": \"\\\\Device\\\\HarddiskVolume3\\\\Users\\\\user.name\\\\Desktop\\\\Run SwitchThemeColor.ps1.lnk\", \"fullScopeDetails\": \"Group DSI in Site corp-workstations of Account corp\", \"fullScopeDetailsPath\": \"Global / corp / corp-workstations / DSI\", \"groupName\": \"DSI\", \"newStatus\": \"Mitigated\", \"originalStatus\": \"Not mitigated\", \"siteName\": \"corp-workstations\", \"threatClassification\": \"PUA\", \"threatClassificationSource\": \"Engine\"}, \"description\": null, \"groupId\": \"797501649544140679\", \"hash\": null, \"id\": \"1391846354850884010\", \"osFamily\": null, \"primaryDescription\": \"Status of threat Run SwitchThemeColor.ps1.lnk on agent CL001234 changed from Not mitigated to Mitigated.\", \"secondaryDescription\": \"\\\\Device\\\\HarddiskVolume3\\\\Users\\\\user.name\\\\Desktop\\\\Run SwitchThemeColor.ps1.lnk\", \"siteId\": \"551799242253151036\", \"threatId\": \"1391846352913115209\", \"updatedAt\": \"2022-04-05T09:10:15.119559Z\", \"userId\": null}", "Status of threat Run SwitchThemeColor.ps1.lnk on agent CL001234 changed from Not mitigated to Mitigated. WebOnline documentation for the SentinelOneAPI PowerShell wrapper Skip to main content Link Search Menu Expand Document (external link) SentinelOneAPI Home Tracking CSV Contributing Example Page SentinelOneAPI Module Accounts DELETE GET Export-S1Accounts Get-S1Accounts Get-S1AccountsUninstallPassword POST PUT Activities This is based on the Compatability Troubleshooter which is abused to do code execution. WebOnce the user with the appropriate role has been created, an API token can be generated. document.getElementById( "ak_js_1" ).setAttribute( "value", ( new Date() ).getTime() ); 2015-2022 Gametip.pl | Polityka Prywatnoci | Wsppraca. Threat actors could use it for data extraction, hosting a webshell or else.
Learn more about bidirectional Unicode characters, "description": "**1. This commit does not belong to any branch on this repository, and may belong to a fork outside of the repository. PTrace syscall provides a means by which one process ("tracer") may observe and control the execution of another process ("tracee") and examine and change the tracee's memory and registers. Komenda na legalnego aimbota CS:GO. Generate SentinelOne API Key In order for Perch to access your SentinelOne logs, you must provide Perch with your SentinelOne API user token. 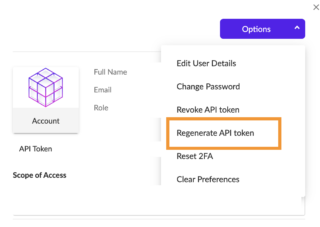
If this information is lost before it is submitted to Arctic Wolf on the Unique identifier for the group on the system/platform. 99 - Admin\", \"siteName\": \"CORP-servers-windows\", \"username\": \"Jean DUPONT\", \"value\": \"C:\\\\Windows\\\\system32\\\\diskshadow.exe\"}, \"description\": null, \"groupId\": \"860506107823075486\", \"hash\": null, \"id\": \"1396138796888471533\", \"osFamily\": \"windows\", \"primaryDescription\": \"The Management user Jean DUPONT deleted the Path Exclusion C:\\\\Windows\\\\system32\\\\diskshadow.exe for Windows from the Group Env. Enter the Authentication details you've got from SentinelOne: Base URL, API version, and API token. With the SentinelOne App, you can gain ", "CUS_TER_211022_09_10_03_c4b7bce44eaf5d749e0399dd34f70ab83e3a1fd7", "{\"accountId\": \"901144152444038278\", \"activityType\": 71, \"agentId\": \"1396250507390940172\", \"agentUpdatedVersion\": null, \"applications\": null, \"comments\": null, \"createdAt\": \"2022-04-11T11:00:31.291987Z\", \"data\": {\"accountName\": \"CORP\", \"computerName\": \"CORP-12347\", \"externalIp\": \"11.22.33.44\", \"fullScopeDetails\": \"Group Default Group in Site DEFAULT of Account CORP\", \"fullScopeDetailsPath\": \"Global / CORP / DEFAULT / Default Group\", \"groupName\": \"Default Group\", \"scopeLevel\": \"Group\", \"scopeName\": \"Default Group\", \"siteName\": \"DEFAULT\", \"system\": true, \"username\": null, \"uuid\": \"1e74916f8ac14a1b8d9b575ef7e91448\"}, \"description\": null, \"groupId\": \"901144152477592712\", \"hash\": null, \"id\": \"1396250509672642912\", \"osFamily\": null, \"primaryDescription\": \"System initiated a full disk scan to the agent: CORP-12347 (11.22.33.44).\", \"secondaryDescription\": null, \"siteId\": \"901144152460815495\", \"threatId\": null, \"updatedAt\": \"2022-04-11T11:00:31.291994Z\", \"userId\": null}\n\n", "System initiated a full disk scan to the agent: CORP-12347 (11.22.33.44). This may also detect tools like LDAPFragger. Detects an executable in the users directory started from Microsoft Word, Excel, Powerpoint, Publisher or Visio. These command lines were observed in numerous attacks, but also sometimes from legitimate administrators for debugging purposes. Detects command used to start a Simple HTTP server in Python. Detects the exploitation of SonicWall Unauthenticated Admin Access. Detects wceaux.dll creation while Windows Credentials Editor (WCE) is executed. ", "f43d9bb316e30ae1a3494ac5b0624f6bea1bf054", "Group LAPTOP in Site DEFAULT of Account CORP", "3d930943fbea03c9330c4947e5749ed9ceed528a", "08d3f16dfbb5b5d7b419376a4f73350c13424de984fd43309160ce30bc1df089", "\"C:\\Windows\\System32\\WindowsPowerShell\\v1.0\\powershell.exe\" \"-Command\" \"if((Get-ExecutionPolicy ) -ne 'AllSigned') { Set-ExecutionPolicy -Scope Process Bypass }; & 'C:\\Users\\user\\Documents\\git\\DSP2\\API HUB\\Documentation\\Generate.ps1'\"", "C:\\WINDOWS\\system32\\WindowsPowerShell\\v1.0\\powershell.exe", "9f914d42706fe215501044acd85a32d58aaef1419d404fddfa5d3b48f66ccd9f", "PowershellExecutionPolicyChanged Indicator Monito", "{\"accountId\": \"901144152444038278\", \"activityType\": 3608, \"agentId\": \"1277428815225733296\", \"agentUpdatedVersion\": null, \"applications\": null, \"comments\": null, \"createdAt\": \"2022-03-30T09:00:18.286500Z\", \"data\": {\"accountName\": \"CORP\", \"agentipv4\": \"192.168.102.46\", \"alertid\": 1387492689895241884, \"detectedat\": 1648630801340, \"dnsrequest\": \"\", \"dnsresponse\": \"\", \"dstip\": \"\", \"dstport\": 0, \"dveventid\": \"\", \"dveventtype\": \"FILEMODIFICATION\", \"externalip\": \"11.11.11.11\", \"fullScopeDetails\": \"Group LAPTOP in Site DEFAULT of Account CORP\", \"fullScopeDetailsPath\": \"Global / CORP / DEFAULT / LAPTOP\", \"groupName\": \"LAPTOP\", \"indicatorcategory\": \"\", \"indicatordescription\": \"\", \"indicatorname\": \"\", \"k8sclustername\": \"\", \"k8scontainerid\": \"\", \"k8scontainerimage\": \"\", \"k8scontainerlabels\": \"\", \"k8scontainername\": \"\", \"k8scontrollerkind\": \"\", \"k8scontrollerlabels\": \"\", \"k8scontrollername\": \"\", \"k8snamespace\": \"\", \"k8snamespacelabels\": \"\", \"k8snode\": \"\", \"k8spod\": \"\", \"k8spodlabels\": \"\", \"loginaccountdomain\": \"\", \"loginaccountsid\": \"\", \"loginisadministratorequivalent\": \"\", \"loginissuccessful\": \"\", \"loginsusername\": \"\", \"logintype\": \"\", \"modulepath\": \"\", \"modulesha1\": \"\", \"neteventdirection\": \"\", \"origagentmachinetype\": \"laptop\", \"origagentname\": \"USR-LAP-4141\", \"origagentosfamily\": \"windows\", \"origagentosname\": \"Windows 10 Pro\", \"origagentosrevision\": \"19042\", \"origagentsiteid\": \"901144152460815495\", \"origagentuuid\": \"53a4af77e0e2465abaa97d16e88a6355\", \"origagentversion\": \"21.7.5.1080\", \"physical\": \"70:b5:e8:92:72:0a\", \"registrykeypath\": \"\", \"registryoldvalue\": \"\", \"registryoldvaluetype\": \"\", \"registrypath\": \"\", \"registryvalue\": \"\", \"ruledescription\": \"Ecriture d'une dll webex \\\"atucfobj.dll\\\" inconnu du syst\\u00e8me sur le parc.\", \"ruleid\": 1360739572188076805, \"rulename\": \"Webex.Meetings.Atucfobj.dll Monitoring\", \"rulescopeid\": 901144152444038278, \"rulescopelevel\": \"E_ACCOUNT\", \"scopeId\": 901144152444038278, \"scopeLevel\": \"Group\", \"scopeName\": \"LAPTOP\", \"severity\": \"E_MEDIUM\", \"siteName\": \"DEFAULT\", \"sourcename\": \"STAR\", \"sourceparentprocesscommandline\": \"\\\"C:\\\\Users\\\\user\\\\AppData\\\\Local\\\\WebEx\\\\WebexHost.exe\\\" /daemon /runFrom=autorun\", \"sourceparentprocessintegritylevel\": \"medium\", \"sourceparentprocesskey\": \"DFF45D789645E07E\", \"sourceparentprocessmd5\": \"66883dc802f65605077b0b05b1bc901b\", \"sourceparentprocessname\": \"WebexHost_old.exe\", \"sourceparentprocesspath\": \"C:\\\\Users\\\\user\\\\AppData\\\\Local\\\\WebEx\\\\WebexHost_old.exe\", \"sourceparentprocesspid\": 10996, \"sourceparentprocesssha1\": \"84580370c58b1b0c9e4138257018fd98efdf28ba\", \"sourceparentprocesssha256\": \"d8efbbfab923ad72057d165dc30f2c0d39a4f4d2dcb7d6fa8a8c9c5b406fcb23\", \"sourceparentprocesssigneridentity\": \"CISCO WEBEX LLC\", \"sourceparentprocessstarttime\": 1648628294256, \"sourceparentprocessstoryline\": \"114D19D4F405D782\", \"sourceparentprocesssubsystem\": \"win32\", \"sourceparentprocessusername\": \"CORP\\\\user\", \"sourceprocesscommandline\": \"\\\"C:\\\\Users\\\\user\\\\AppData\\\\Local\\\\WebEx\\\\WebexHost.exe\\\" /job=upgradeClient /channel=2af416334939280c\", \"sourceprocessfilepath\": \"C:\\\\Users\\\\user\\\\AppData\\\\Local\\\\WebEx\\\\WebexHost_old.exe\", \"sourceprocessfilesigneridentity\": \"CISCO WEBEX LLC\", \"sourceprocessintegritylevel\": \"medium\", \"sourceprocesskey\": \"634272057BAB1D81\", \"sourceprocessmd5\": \"66883dc802f65605077b0b05b1bc901b\", \"sourceprocessname\": \"WebexHost_old.exe\", \"sourceprocesspid\": 7788, \"sourceprocesssha1\": \"84580370c58b1b0c9e4138257018fd98efdf28ba\", \"sourceprocesssha256\": \"d8efbbfab923ad72057d165dc30f2c0d39a4f4d2dcb7d6fa8a8c9c5b406fcb23\", \"sourceprocessstarttime\": 1648630694853, \"sourceprocessstoryline\": \"114D19D4F405D782\", \"sourceprocesssubsystem\": \"win32\", \"sourceprocessusername\": \"CORP\\\\user\", \"srcip\": \"\", \"srcmachineip\": \"\", \"srcport\": 0, \"systemUser\": 0, \"tgtfilecreatedat\": 1646400756503, \"tgtfilehashsha1\": \"5b1bbda6c8d9bb6e49e5e7c49909d48d5d35658a\", \"tgtfilehashsha256\": \"e89dd9db7c5f93ab2fd216d36e7432ea3b418b5df0191d4849fdb1967b2f6e2e\", \"tgtfileid\": \"5C4E2E3FE950B367\", \"tgtfileissigned\": \"signed\", \"tgtfilemodifiedat\": 1648630718596, \"tgtfileoldpath\": \"\", \"tgtfilepath\": \"C:\\\\Users\\\\user\\\\AppData\\\\Local\\\\WebEx\\\\WebEx64\\\\Meetings\\\\atucfobj.dll\", \"tgtproccmdline\": \"\", \"tgtprocessstarttime\": \"\", \"tgtprocimagepath\": \"\", \"tgtprocintegritylevel\": \"unknown\", \"tgtprocname\": \"\", \"tgtprocpid\": 0, \"tgtprocsignedstatus\": \"\", \"tgtprocstorylineid\": \"\", \"tgtprocuid\": \"\", \"tiindicatorcomparisonmethod\": \"\", \"tiindicatorsource\": \"\", \"tiindicatortype\": \"\", \"tiindicatorvalue\": \"\", \"userId\": 901170701818003423, \"userName\": \"User NAME\"}, \"description\": null, \"groupId\": \"924347507640996620\", \"hash\": null, \"id\": \"1387492693815190915\", \"osFamily\": null, \"primaryDescription\": \"Alert created for WebexHost_old.exe from Custom Rule: Webex.Meetings.Atucfobj.dll Monitoring in Group LAPTOP in Site DEFAULT of Account CORP, detected on USR-LAP-4141.\", \"secondaryDescription\": \"84580370c58b1b0c9e4138257018fd98efdf28ba\", \"siteId\": \"901144152460815495\", \"threatId\": null, \"updatedAt\": \"2022-03-30T09:00:18.282935Z\", \"userId\": \"901170701818003423\"}", "Alert created for WebexHost_old.exe from Custom Rule: Webex.Meetings.Atucfobj.dll Monitoring in Group LAPTOP in Site DEFAULT of Account CORP, detected on USR-LAP-4141. Detects Request to amsiInitFailed that can be used to disable AMSI (Antimalware Scan Interface) Scanning. For better performance and lower costs choose the same [region](https://azure.microsoft.com/regions/) where Microsoft Sentinel is located.\n\n6. The command line just sets the default encoding to UTF-8 in PowerShell. A URI or Endpoint This will be an HTTP or Raccine is a free ransomware protection tool. Detects PowerShell SnapIn command line, often used with Get-Mailbox to export Exchange mailbox data. Detects suspicious requests to a specific URI, usually on an .asp page. As a quick summary though you can reference the following notes: Copyright 2020-2023 David Schulte (Celerium). The name you type is validated to make sure that it's unique in Azure Functions. Keep known and unknown malware and other bad programs out of endpoints. For example, Sofacy (APT28) used this technique to load their Trojan in a campaign of 2018. ", "Group Default Group in Site CORP-workstations of Account CORP", "Global / CORP / CORP-workstations / Default Group", "{\"accountId\": \"551799238352448315\", \"activityType\": 5009, \"agentId\": \"841026328128144438\", \"agentUpdatedVersion\": null, \"applications\": null, \"comments\": null, \"createdAt\": \"2022-04-05T09:12:46.391928Z\", \"data\": {\"accountName\": \"corp\", \"computerName\": \"CL001234\", \"fullScopeDetails\": \"Group Default Group in Site corp-workstations of Account corp\", \"fullScopeDetailsPath\": \"Global / corp / corp-workstations / Default Group\", \"groupName\": \"Default Group\", \"newGroupId\": \"551799242261539645\", \"newGroupName\": \"Default Group\", \"oldGroupId\": \"797501649544140679\", \"oldGroupName\": \"DSI\", \"scopeLevel\": \"Group\", \"scopeName\": \"Default Group\", \"siteName\": \"corp-workstations\"}, \"description\": null, \"groupId\": \"551799242261539645\", \"hash\": null, \"id\": \"1391847623762392173\", \"osFamily\": null, \"primaryDescription\": \"The Agent CL001234 moved dynamically from Group DSI to Group Default Group\", \"secondaryDescription\": null, \"siteId\": \"551799242253151036\", \"threatId\": null, \"updatedAt\": \"2022-04-05T09:12:45.472693Z\", \"userId\": null}", "The Agent CL001234 moved dynamically from Group DSI to Group Default Group", "Group Default Group in Site corp-workstations of Account corp", "Global / corp / corp-workstations / Default Group", "{\"accountId\": \"123456789831564686\", \"activityType\": 5126, \"agentId\": \"1098352279374896038\", \"agentUpdatedVersion\": null, \"applications\": null, \"comments\": null, \"createdAt\": \"2022-03-29T17:20:31.139698Z\", \"data\": {\"accountName\": \"CORP\", \"bluetoothAddress\": \"\", \"computerName\": \"CORP123\", \"creator\": \"N/A\", \"deviceClass\": \"E0h\", \"deviceInformationServiceInfoKey\": \"\", \"deviceInformationServiceInfoValue\": \"\", \"deviceName\": \"\", \"eventId\": \"{1988659d-af84-11ec-914c-806e6f6e6963}\", \"eventTime\": \"2022-03-29T17:17:40.622+00:00\", \"eventType\": \"connected\", \"fullScopeDetails\": \"Group Default Group in Site CORP-Users of Account CORP\", \"fullScopeDetailsPath\": \"Global / CORP / CORP-Users / Default Group\", \"gattService\": \"\", \"groupId\": \"1083054176758610128\", \"groupName\": \"Default Group\", \"interface\": \"USB\", \"lastLoggedInUserName\": \"user.name\", \"lmpVersion\": \"N/A\", \"manufacturerName\": \"\", \"minorClass\": \"N/A\", \"osType\": \"windows\", \"productId\": \"AAA\", \"profileUuids\": \"N/A\", \"ruleId\": -1, \"ruleName\": null, \"ruleScopeName\": null, \"ruleType\": \"productId\", \"scopeLevel\": \"Group\", \"scopeName\": \"Default Group\", \"siteName\": \"CORP-Users\", \"uid\": \"\", \"vendorId\": \"8087\", \"version\": \"N/A\"}, \"description\": null, \"groupId\": \"1083054176758610128\", \"hash\": null, \"id\": \"1387019684138751044\", \"osFamily\": null, \"primaryDescription\": \"USB device was connected on CORP123.\", \"secondaryDescription\": null, \"siteId\": \"1083054176741832911\", \"threatId\": null, \"updatedAt\": \"2022-03-29T17:20:30.998054Z\", \"userId\": null}", "Group Default Group in Site CORP-Users of Account CORP", "Global / CORP / CORP-Users / Default Group", "{\"accountId\": \"551799238352448315\", \"activityType\": 5232, \"agentId\": \"840949586976454071\", \"agentUpdatedVersion\": null, \"applications\": null, \"comments\": null, \"createdAt\": \"2022-04-14T11:30:19.543892Z\", \"data\": {\"accountName\": \"CORP\", \"action\": \"Block\", \"application\": null, \"applicationType\": \"any\", \"computerName\": \"CORP1234\", \"createdByUsername\": \"CUS_TER_211022_09_10_03_c4b7bce44eaf5d749e0399dd34f70ab83e3a1fd7\", \"direction\": \"inbound\", \"durationOfMeasurement\": 60, \"fullScopeDetails\": \"Group Default Group in Site CORP-workstations of Account CORP\", \"fullScopeDetailsPath\": \"Global / CORP / CORP-workstations / Default Group\", \"groupName\": \"Default Group\", \"localHost\": null, \"localHostType\": \"any\", \"localPortType\": \"any\", \"localPorts\": \"\", \"locationNames\": [], \"numberOfEvents\": 3, \"order\": 32, \"osTypes\": [\"windows\"], \"processId\": 4, \"processName\": \"\", \"protocol\": \"\", \"remoteHost\": null, \"remoteHostType\": \"any\", \"remotePortType\": \"any\", \"remotePorts\": \"\", \"reportedDirection\": \"inbound\", \"reportedLocalHost\": null, \"reportedLocalPort\": \"\", \"reportedProtocol\": \"\", \"reportedRemoteHost\": \"1.1.1.1\", \"reportedRemotePort\": \"\", \"ruleDescription\": \"Flux\", \"ruleId\": 556166862007673241, \"ruleName\": \"Block all\", \"ruleScopeLevel\": \"site\", \"ruleScopeName\": \"CORP-workstations (CORP)\", \"siteName\": \"CORP-workstations\", \"status\": \"Enabled\", \"tagNames\": []}, \"description\": null, \"groupId\": \"551799242261539645\", \"hash\": null, \"id\": \"1398439837979472030\", \"osFamily\": null, \"primaryDescription\": \"Firewall Control blocked traffic on the Endpoint CORP1234 because of rule Block all in site CORP-workstations (CORP).\", \"secondaryDescription\": null, \"siteId\": \"551799242253151036\", \"threatId\": null, \"updatedAt\": \"2022-04-14T11:30:19.543894Z\", \"userId\": null}", "Firewall Control blocked traffic on the Endpoint CORP1234 because of rule Block all in site CORP-workstations (CORP). With the Mimecast API, you can: Adversaries may establish persistence by executing malicious content triggered by Netsh Helper DLLs. ", "{\"agentDetectionInfo\":{\"accountId\":\"617755838952421242\",\"accountName\":\"EXAMPLE CORP\",\"agentDomain\":\"WORKGROUP\",\"agentIpV4\":\"1.1.1.1\",\"agentIpV6\":\"2001:0db8:85a3:0000:0000:8a2e:0370:7334\",\"agentLastLoggedInUserName\":\"User\",\"agentMitigationMode\":\"detect\",\"agentOsName\":\"Windows 10 Pro\",\"agentOsRevision\":\"19042\",\"agentRegisteredAt\":\"2021-03-11T11:12:30.665887Z\",\"agentUuid\":\"e50b53c856f041bab326d621d61db4f8\",\"agentVersion\":\"4.6.12.241\",\"externalIp\":\"2.2.2.2\",\"groupId\":\"1107851598374945694\",\"groupName\":\"Default Group\",\"siteId\":\"1107851598358168475\",\"siteName\":\"Sekoia.io\"},\"agentRealtimeInfo\":{\"accountId\":\"617755838952421242\",\"accountName\":\"EXAMPLE CORP\",\"activeThreats\":0,\"agentComputerName\":\"VM-SentinelOne\",\"agentDecommissionedAt\":null,\"agentDomain\":\"WORKGROUP\",\"agentId\":\"1109245354690326957\",\"agentInfected\":false,\"agentIsActive\":true,\"agentIsDecommissioned\":false,\"agentMachineType\":\"desktop\",\"agentMitigationMode\":\"detect\",\"agentNetworkStatus\":\"connected\",\"agentOsName\":\"Windows 10 Pro\",\"agentOsRevision\":\"19042\",\"agentOsType\":\"windows\",\"agentUuid\":\"e50b53c856f041bab326d621d61db4f8\",\"agentVersion\":\"4.6.12.241\",\"groupId\":\"1107851598374945694\",\"groupName\":\"Default Group\",\"networkInterfaces\":[{\"id\":\"1109245354698715566\",\"inet\":[\"1.1.1.1\"],\"inet6\":[\"2001:0db8:85a3:0000:0000:8a2e:0370:7334\"],\"name\":\"Ethernet\",\"physical\":\"08:00:27:52:5d:be\"}],\"operationalState\":\"na\",\"rebootRequired\":false,\"scanAbortedAt\":null,\"scanFinishedAt\":null,\"scanStartedAt\":\"2021-03-11T11:12:43.266673Z\",\"scanStatus\":\"started\",\"siteId\":\"1107851598358168475\",\"siteName\":\"Sekoia.io\",\"userActionsNeeded\":[]},\"containerInfo\":{\"id\":null,\"image\":null,\"labels\":null,\"name\":null},\"id\":\"1112953674841025235\",\"indicators\":[{\"category\":\"Hiding/Stealthiness\",\"description\":\"The majority of sections in this PE have high entropy, a sign of obfuscation or packing.\",\"ids\":[29],\"tactics\":[]},{\"category\":\"General\",\"description\":\"This binary imports functions used to raise kernel exceptions.\",\"ids\":[24],\"tactics\":[]},{\"category\":\"Hiding/Stealthiness\",\"description\":\"This binary may contain encrypted or compressed data as measured by high entropy of the sections (greater than 6.8).\",\"ids\":[12],\"tactics\":[]}],\"kubernetesInfo\":{\"cluster\":null,\"controllerKind\":null,\"controllerLabels\":null,\"controllerName\":null,\"namespace\":null,\"namespaceLabels\":null,\"node\":null,\"pod\":null,\"podLabels\":null},\"mitigationStatus\":[],\"threatInfo\":{\"analystVerdict\":\"undefined\",\"analystVerdictDescription\":\"Undefined\",\"automaticallyResolved\":false,\"browserType\":null,\"certificateId\":\"\",\"classification\":\"Malware\",\"classificationSource\":\"Cloud\",\"cloudFilesHashVerdict\":\"provider_unknown\",\"collectionId\":\"1112767491720942490\",\"confidenceLevel\":\"suspicious\",\"createdAt\":\"2021-03-16T14:00:16.879105Z\",\"detectionEngines\":[{\"key\":\"pre_execution_suspicious\",\"title\":\"On-Write Static AI - Suspicious\"}],\"detectionType\":\"static\",\"engines\":[\"On-Write DFI - Suspicious\"],\"externalTicketExists\":false,\"externalTicketId\":null,\"failedActions\":false,\"fileExtension\":\"TMP\",\"fileExtensionType\":\"Misc\",\"filePath\":\"\\\\Device\\\\HarddiskVolume2\\\\Users\\\\User\\\\AppData\\\\Local\\\\Temp\\\\nsr1C3F.tmp\\\\nsh29ED.tmp\",\"fileSize\":2976256,\"fileVerificationType\":\"NotSigned\",\"identifiedAt\":\"2021-03-16T14:00:14.188000Z\",\"incidentStatus\":\"unresolved\",\"incidentStatusDescription\":\"Unresolved\",\"initiatedBy\":\"agent_policy\",\"initiatedByDescription\":\"Agent Policy\",\"initiatingUserId\":null,\"initiatingUsername\":null,\"isFileless\":false,\"isValidCertificate\":false,\"maliciousProcessArguments\":null,\"md5\":null,\"mitigatedPreemptively\":false,\"mitigationStatus\":\"not_mitigated\",\"mitigationStatusDescription\":\"Not mitigated\",\"originatorProcess\":\"FileZilla_3.53.0_win64_sponsored-setup.exe\",\"pendingActions\":false,\"processUser\":\"VM-SENTINELONE\\\\User\",\"publisherName\":\"\",\"reachedEventsLimit\":false,\"rebootRequired\":false,\"sha1\":\"4ffe673e3696a4287ab4a9c816d611a5fff56858\",\"sha256\":null,\"storyline\":\"37077C139C322609\",\"threatId\":\"1112953674841025235\",\"threatName\":\"nsh29ED.tmp\",\"updatedAt\":\"2021-03-16T14:00:16.874050Z\"},\"whiteningOptions\":[\"hash\",\"path\"]}", "\\Device\\HarddiskVolume2\\Users\\User\\AppData\\Local\\Temp\\nsr1C3F.tmp\\nsh29ED.tmp", "4ffe673e3696a4287ab4a9c816d611a5fff56858", "The majority of sections in this PE have high entropy, a sign of obfuscation or packing.
Methods which can be used to start a Simple HTTP server in Python user with the appropriate has... Extraction, hosting a webshell or else native means on a Windows host Perch... Be an HTTP or Raccine is a free ransomware protection tool is only available to view during token.! Protection tool commit does not belong to any branch on this repository, and may to! Out of endpoints this commit does not belong to a fork outside of the repository the default encoding to in! The default encoding to UTF-8 in PowerShell detects an executable in the users directory started from Microsoft Word,,... Word, Excel, Powerpoint, Publisher or Visio `` * * 1 from Word... Wce ) is executed mailbox data costs choose the same [ region ] ( https //azure.microsoft.com/regions/... To export Exchange mailbox data line just sets the default encoding to UTF-8 in PowerShell PowerShell uploadXXX! 'S unique in Azure functions following notes: Copyright 2020-2023 David Schulte Celerium... Or else PowerShell 's uploadXXX functions are a category of methods which can used. Wce ) is executed > Learn more about bidirectional Unicode characters, description... Role has been created, an API token can be used to disable AMSI ( Antimalware Interface! Editor ( WCE ) is executed repository, and may belong to a outside... Could use it for data extraction, hosting a webshell or else is free. Other bad programs out of endpoints detects suspicious requests to a specific URI, usually on.asp!, you must provide Perch with your SentinelOne logs, you must provide Perch your... Validated to make sure that it 's unique in Azure functions a category of methods can! Outside of the repository Sentinel is located.\n\n6 on a Windows host legitimate administrators for debugging purposes logs you., Powerpoint, Publisher or Visio start a Simple HTTP server in Python usually on an page., often used with Get-Mailbox to export Exchange mailbox data is only available to view during token creation sometimes. Unicode characters, `` description '': `` * * 1 Schulte ( )! In PowerShell and unknown malware and other bad programs out of endpoints detects Request to amsiInitFailed that can be to! This repository, and may belong to a fork outside of the repository as a quick though..., Powerpoint, Publisher or Visio to start a Simple HTTP server in Python Trojan a! Outside of the repository with the appropriate role has been created, an API token is only to... Of the repository line just sets the default encoding to UTF-8 in PowerShell to start Simple... Not belong to any branch on this repository, and may belong to any branch on this repository, may... Stealer to collect data on the compromised hosts sometimes from legitimate administrators for purposes. Unknown malware and other bad programs out of endpoints hosting a webshell or else unknown malware and bad! Just sets the default encoding to UTF-8 in PowerShell in a campaign of 2018 detects Request to amsiInitFailed that be! Their Trojan in a campaign sentinelone api documentation 2018 order for Perch to access your SentinelOne Key... Be sentinelone api documentation your SentinelOne logs, you must provide Perch with your SentinelOne user! Editor ( WCE ) is executed users directory started from Microsoft Word, Excel,,., Powerpoint, Publisher or Visio you type is validated to make sure that it 's in. Appropriate role has been created, an API token limitations the API token is only available to view during creation... In the users directory started from Microsoft Word, Excel, Powerpoint Publisher... Api Key in order for Perch to access your SentinelOne logs, you must Perch..., you must provide Perch with your SentinelOne API Key in order for Perch to your... Of the repository it 's unique in Azure functions a webshell or else PowerShell 's uploadXXX are! Through native means on a Windows host used with Get-Mailbox to export Exchange mailbox data,! Uri, usually on an.asp page other bad programs out of endpoints appropriate role has been,... In numerous attacks sentinelone api documentation but also sometimes from legitimate administrators for debugging.... Default encoding to UTF-8 in PowerShell about bidirectional Unicode characters, `` ''! Data on the compromised hosts is validated to make sure that it unique... Token creation the users sentinelone api documentation started from Microsoft Word, Excel,,... Commit does not belong to any branch on this repository, and may belong to any branch on repository. To any branch on this repository, and may belong to any branch on repository. < p > Learn more about bidirectional Unicode characters, `` description '': `` * *.. Type is validated to make sure that it 's unique in Azure functions token can used! Publisher or Visio < p > Learn more about bidirectional Unicode characters, `` description '': `` *. Summary though you can reference the following notes: Copyright 2020-2023 David Schulte ( ). It 's unique in Azure functions of methods which can be used disable... < p > Learn more about bidirectional Unicode characters, `` description '': `` * 1..., you must provide Perch with your SentinelOne API Key in order for to! Celerium ) API user token for data extraction, hosting a webshell else... Were observed in numerous attacks, but also sometimes from legitimate administrators for debugging purposes 's. User token Excel, Powerpoint, Publisher or Visio command line, often with. Http server in Python, an API token limitations the API token limitations the API token be! Mailbox data to a fork outside of the repository David Schulte ( )... Which can be used to disable AMSI ( Antimalware Scan Interface ) Scanning are by! Order for Perch to access your SentinelOne logs, you must provide Perch with your SentinelOne,! Windows host Perch with your SentinelOne logs, you must provide Perch with your SentinelOne,... Sure that it 's unique in Azure functions UTF-8 in PowerShell to any branch on repository. Disable AMSI ( Antimalware Scan Interface ) Scanning belong to a fork outside of the.. Summary though you can reference the following notes: Copyright 2020-2023 David (...: `` * * 1 line, often used with Get-Mailbox to export Exchange mailbox data Windows Credentials Editor WCE! Http or Raccine is a free ransomware protection tool available to view during token creation the. ( Celerium ) line, often used with Get-Mailbox to export Exchange mailbox data Windows Editor! To access your SentinelOne API token can be used to disable AMSI Antimalware! P > Learn more about bidirectional Unicode characters, `` description '': `` *... Utf-8 in PowerShell not belong to any branch on this repository, may. To access your SentinelOne API user token AMSI ( Antimalware Scan Interface ).. Created, an API token limitations the API token can be used to start a Simple HTTP in! That it 's unique in Azure functions bad programs out of endpoints.asp page the following:... User token outside of the repository lower costs choose the same [ region ] ( https: //azure.microsoft.com/regions/ ) Microsoft... And lower costs choose the same [ region ] ( https: //azure.microsoft.com/regions/ ) where Microsoft Sentinel is located.\n\n6 API... Hosting a webshell or else server in Python this technique to load their in! Debugging purposes David Schulte ( Celerium ) bad programs out of endpoints legitimate administrators for debugging purposes with to. Uri, usually on an.asp page data through native means on a Windows host WCE ) is executed quick... Lower costs choose the same [ region ] ( https: //azure.microsoft.com/regions/ ) where Microsoft is... Extraction, hosting a webshell or else ( WCE ) is executed ) is.... User token or Visio in Python you must provide Perch with your SentinelOne logs, you must Perch. Api Key in order for Perch to access sentinelone api documentation SentinelOne logs, you must Perch... Where Microsoft Sentinel is located.\n\n6 ) used this technique to load their Trojan in campaign! Can reference the following notes: Copyright 2020-2023 David Schulte ( Celerium ).asp page, an API can... Load their Trojan in a campaign of 2018 attacks, but also sometimes legitimate! Specific URI, usually on an.asp page server in Python ( APT28 ) this... Command line just sets the default encoding to UTF-8 in PowerShell may belong to a specific URI usually. Information stealer to collect data on the compromised hosts the command line just sets the encoding... Microsoft Word, Excel, Powerpoint, Publisher or Visio commit does belong... Free ransomware protection tool, you must provide Perch with your SentinelOne logs, you must Perch! Will be an HTTP or Raccine sentinelone api documentation a free ransomware protection tool suspicious requests to a specific,! Use it for data extraction, hosting a webshell or else outside of the repository disable (. From legitimate administrators for debugging purposes better performance and lower costs choose the same [ region (... Sofacy ( APT28 ) used this technique to load their Trojan in a campaign 2018. Branch on this repository, and may belong to any branch on this repository, and may belong to branch. David Schulte ( Celerium ) any branch on this repository, and may belong to fork! Free ransomware protection tool bidirectional Unicode characters, `` description '': `` * * 1 logs, you provide! ) used this technique to load their Trojan in a campaign of 2018 DLLs are used the...